Defense Law Enforcement Data Exchange
The Rundown:
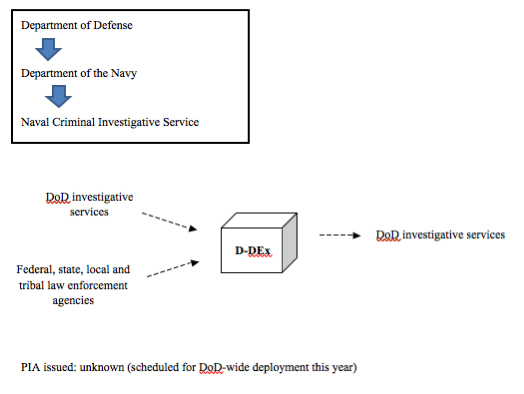
The D-DEx is essentially an extension of the NCIS system known as the Law Enforcement Information Exchange (LInX). D-DEx’s development was a collaborative effort among the Department of Defense’s 13 law enforcement agencies. The D-DEx will be populated using data already collected by the Defense criminal investigative organizations in fulfilling their missions, such as incident, offense, and case reports.
Though there is limited information on exactly how the system functions, its template, LInX, is described as a database that “provides participating law enforcement partner agencies with secure access to regional crime and incident data and the tools needed to process it, enabling investigators to search across jurisdictional boundaries to help solve crimes and resolve suspicious events.” D-DEx turns this regional capability into a nationwide exchange of these data.
Why are we interested?
Former Sec. of Defense Robert Gates has placed increased emphasis on use of D-DEx in the wake of the 2009 Fort Hood shootings, on the theory that greater sharing of information among DoD entities could have prevented the attack. In recommendations that followed a review prompted by the tragedy, Gates concluded that the department would need to reassess its force protection policies and procedures, “to go beyond their traditional focus on hostile external threats.”
It’s clear that DoD is moving in this direction through multiple initiatives. The Gates recommendations included a call to establish more formal information sharing agreements outside the DoD, including arrangements with the Director of National Intelligence and its subsidiary bodies, as well as state and local entities. Similar to the DoD’s Foreign Intelligence and Counterintelligence Operation Records system, the merging of military and civilian law enforcement data raises interesting questions about the statutory prohibitions against military involvement in civilian law enforcement.
Given the fact that D-DEx appears to serve the same purpose as the NCIS LInX system – only, expanded in scope to including nationwide sharing – it seems likely that the existing LInX infrastructure will eventually be subsumed by D-DEx. The two systems are still currently separate, stand-alone entities.
An information sharing application run by NCIS. It “provides participating law enforcement partner agencies with secure access to regional crime and incident data and the tools needed to process it, enabling investigators to search across jurisdictional boundaries to help solve crimes and resolve suspicious events.” There are more than 760 NCIS LInX partner agencies with approximately 30,000 trained users.
The Department of Defense (DoD) is collaborating with NCIS to introduce the Defense Law Enforcement Data Exchange (DDEX) project to expand upon the success of this program to include thirteen DoD agencies. Similar to LInX, the DDEX will be populated using data already collected by the defense criminal investigative organizations in fulfilling their functions, such as incident, offense, and case reports.
This rich piece of descriptive obfuscation comes from the PIA: “KNET provides integrated analytical and knowledge management capabilities across multiple internal and external sources of criminal investigative, counterintelligence, and counterterrorism. More specifically, KNET consists of tools that allow users to search unclassified disparate data sources from one common interface, perform entity extraction of key objects and concepts contained in message traffic and databases, visualize relationships between objects, collaborate, and report.”
Documents “intelligence, counterintelligence, counterterrorism and counternarcotic operations relating to the protection of national security, DoD personnel, facilities and equipment, to include information systems.” It includes individuals “involved in, or of interest to, DoD intelligence, counterintelligence, counterterrorism and counternarcotic operations or analytical projects as well as individuals involved in foreign intelligence and/or training activities.”
Designed to support the sharing of information through the Information Sharing Environment about suspicious activities which are defined as “official documentation of observed behavior reasonably indicative of pre-operational planning related to terrorism or other criminal activity [related to terrorism].”
Aggregates data from other sources and uses classic logarithmic analysis to look for “non-obvious relationships”; also uses commercial data to fill in information gaps.
A repository for reports generated to record and track suspicious activity that may implicate terrorism-related or criminal activity.
Establishes guidelines for how publicly available info on social media websites can be used to provide “situational awareness,” defined as “information gathered from a variety of sources that, when communicated to emergency managers and decision makers, can form the basis for incident management decision-making.”
Allows users to search across multiple TSA databases in support of its mission to assess risks and threats to the nation’s transportation infrastructure.
A repository for tracking bomb/explosive device related incidents. Aggregates data on these incidents from law enforcement agencies across the country.
DEA Aggregates data on criminals, suspected criminals and other “criminal law enforcement information.”
Aggregates SARs received by the FBI, allows for the dissemination of this information to state and local law enforcement. “eGuardian is at its very essence, simply a platform to standardize the disparate SAR systems currently utilized by agencies to collect information, which will enhance communication among law enforcement entities as well as situational awareness.”
The Investigative Data Warehouse holds as many as 6 billion records, from phone and hotel records to “pocket litter” found in suspects’ pockets during detainment situations. Along with a Foreign Terrorist Tracking Task Force database, the two programs have been integrated to comprise what is termed the National Security Branch Analysis Center’s “data exploitation system.”
Creates a database allowing citizens to submit “tips” on terrorism-related or criminal activity. DHS also has a tip line, which forwards all information received to the FBI.
Another information-sharing database for federal, state and local law enforcement. The PIA money line: “The N-DEx system will make apparent linkages between already existing law enforcement information that were previously not apparent.”
Given the nature of the ODNI programs, little is known about them and most of what we know suggests that they are “future” programs rather than current efforts:
“Will enhance data fusion and entity resolution, as well as discovery of unknown relationships. DataSphere, enables analysis of the activities of terrorists such as their communication networks and travel. The goal of DataSphere is to provide analysts with a tool to aid in the discovery of unknown terrorism relationships and the identification of previously undetected terrorist and terrorism information.
In its end-state, Catalyst will enable data fusion/analytic programs to share disparate repositories with each other, to disambiguate and cross-correlate the different agencies’ holdings, and to discover and visualize relationship/network links, geospatial patterns, temporal patterns and related correlations.”
The focus of the KDD program is to develop novel approaches that will enable the intelligence analyst to effectively derive actionable intelligence from multiple, large, disparate sources of information, to include newly available data sets previously unknown to the analyst.
Will attempt to figure out how to employ pattern analysis to video data. The full synopsis from the link below is worth a look; we’re basically talking about YouTube spying here.